“Are you at your desk?” is a small question with an impressive expense account.
It can open a perfectly ordinary work conversation. It can also be an attacker checking whether someone’s available to follow instructions. After the target replies, the fraudulent invoice, new bank account, or supposedly confidential payment request arrives.
APWG’s Q2 2026 report (opens in new tab) shows how much money can ride on the conversation that follows. The average amount requested in wire-transfer BEC attacks reached $61,732, up 45% from the previous quarter. That measures what attackers asked for, rather than what victims ultimately lost. It’s a sizable request to put behind such an unremarkable first message.
Microsoft’s research shows how often these attacks begin without an obvious financial request. Coalition’s claims findings add another wrinkle: a confirmed mailbox compromise isn’t involved in every funds-transfer fraud event. Finance teams need to account for both when deciding what to verify and when.
APWG’s figure comes from BEC attacks observed by contributor Fortra. The reported average wire request rose from $42,663 in Q1 2026 to $61,732 in Q2, a rounded 45% increase. Observed wire-transfer attempts also rose 88% quarter over quarter.
Those signals describe the monitored activity. They aren’t a global count of every BEC attempt, and the average request doesn’t tell us the median request, success rate, amount recovered, or final loss. A larger average could reflect changes in the mix of observed campaigns. It doesn’t establish that every attacker raised their prices.
For accounts payable, the invoice amount is only part of the check. A request can start with a routine exchange and later request bank details. If the review focuses on whether the opening email looks suspicious, the payment instructions may escape the scrutiny they deserve.
Business email compromise succeeds when an employee believes the payment or disclosure request comes from someone they trust. Sometimes the attacker controls that person’s real mailbox. Sometimes a different address and a familiar display name are enough to start the conversation. Investigators need to establish which happened, but finance still has to verify the instruction.
The next question is how that request earns enough trust to reach the payment queue.
The first message is an availability check
Microsoft’s Q1 2026 email threat analysis (opens in new tab) found generic outreach accounted for 82–84% of initial BEC contact emails each month. Its Q2 analysis (opens in new tab) put that range at 87–92%. Across the six monthly observations, the range was therefore 82–92%, rather than one pooled percentage for the entire half-year.
An opener like “Are you at your desk?” asks about availability before presenting payment instructions. It creates a conversation before it creates the financial problem.
A short message without a link or attachment gives the recipient less to inspect. It also looks like something a real colleague might send. Treat the reply as the beginning of a conversation to assess: who’s asking, what do they want next, and does that request depart from the usual approval process?
When the conversation becomes a payment request
Consider this illustrative sequence:
- A familiar name starts the exchange. A supposed executive asks whether a finance employee can help with something.
- The request becomes specific. The sender describes the payment as urgent or sensitive, and a document provides plausible business detail.
- Normal verification becomes inconvenient. The sender claims they’re unavailable for a callback or asks the employee to keep the matter confidential.
- A legitimate user authorizes the transfer. The banking system receives an instruction from someone who really has permission to send money.
Replying doesn’t authorize a payment, but familiarity can make the later request feel already vetted. The callback belongs at that later point, before someone changes a beneficiary or releases funds. It gives finance a chance to check the instruction independently of the person typing in the thread.
Searching the first message for bank details or urgent financial language won’t catch a request that arrives three replies later. Review the conversation as it develops, and make sure employees can report the whole exchange rather than forwarding only the opening line.
A hijacked mailbox is one path to financial fraud
Coalition’s 2026 Cyber Claims Report found 39% of funds-transfer fraud events occurred without confirmed email compromise. The wording deserves care: “no confirmed” compromise doesn’t prove that email was never involved. It also doesn’t mean that all those events were caused by lookalike domains.
The broader category includes financial fraud through other paths. An attacker might misuse financial-system credentials or send fraudulent instructions through a channel outside the mailbox under investigation. A business can lose money even when investigators don’t establish a BEC incident.
Coalition’s public report announcement (opens in new tab) says 52% of its 2025 funds-transfer fraud claims originated from BEC. Some email compromises therefore led to payment fraud, while other payment-fraud claims took a different route. Checking whether a mailbox was breached matters, but it won’t capture every way money can leave.
Keep the insurance findings separate from APWG’s wire-request data. Coalition is describing events and claims in its own portfolio; APWG is reporting attempted requests observed by a contributor. You can compare the problems they reveal, but you can’t combine their percentages to calculate a loss rate or a company’s odds of being hit.
That leaves two investigations to coordinate: how the attacker reached the business, and what happened to the payment. Even if the email investigation finds no compromised account, finance still needs to check the beneficiary record and any transfer already released.
Familiar details can conceal a new instruction
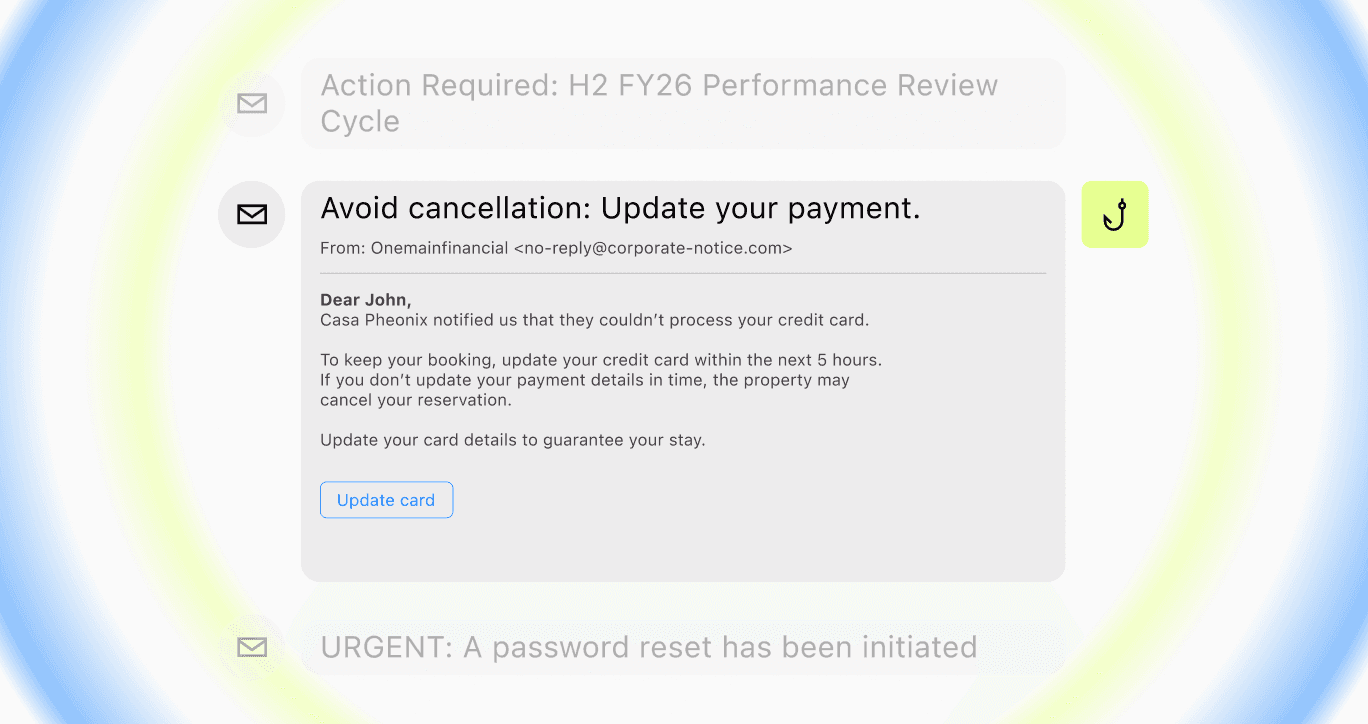
In accounts payable, risky requests often change something real: a genuine supplier, an expected invoice, or an established payment schedule. The amount and purchase order can be correct while the beneficiary account is wrong.
Vendor invoice fraud exploits that combination. Accurate surrounding details make the changed instruction seem less worthy of scrutiny. An attacker doesn’t need to rewrite the entire business relationship. Moving one field can be enough.
Verify the changed instruction through a contact the requester doesn’t control. If the invoice total and purchase order are correct, that confirms those details only. It doesn’t authenticate a new bank account. A reply in the same email thread sends the question straight back to whoever is controlling the conversation.
Watch for combinations such as:
- A payment change plus a deadline. The request creates a reason to skip the ordinary check.
- A familiar display name plus an unfamiliar address. Recognizing the person substitutes for verifying the account.
- A convincing document plus a new beneficiary. Accurate formatting distracts from the instruction that moves the money.
- A follow-up call plus a supplied callback number. Two contacts can still come from one attacker.
Each signal needs context. Their value is in guiding verification, not handing employees another list of suspicious words to memorize.
Put verification where the money changes direction
Under pressure, a finance employee shouldn’t have to invent a way to verify the CFO’s request. The payment procedure should explain how to pause the transfer and where to find a trusted contact, even when the caller insists there isn’t time.
The FBI’s BEC guidance (opens in new tab) recommends verifying payment requests and changes in account numbers or payment procedures with the person making the request. For a business, that means defining how you independently verify before the urgent message arrives.
Establish an independent callback
Use a trusted contact record maintained outside the request. A number included in the new invoice, email signature, or follow-up message can be part of the deception. If you can’t reach the established contact, keep the payment on hold under a documented exception process.
Give finance a way to handle genuine last-minute changes as well. If suppliers routinely send corrections five minutes before cutoff, staff will keep encountering the same pressure attackers exploit. Decide in advance who can hold the payment and how a delayed, legitimate request gets resolved.
Separate changing details from releasing funds
Require independent review for beneficiary changes and clearly assign approval authority. Having two people review the same fraudulent email doesn’t create two independent checks. One person can verify the request through the trusted channel while another confirms the payment follows the approved record.
Apply the check to changes below any high-value approval threshold as well. The APWG average is a headline, not a sensible minimum amount at which to start caring.
Give suspicious requests a fast route to help
Employees should be able to pause a payment and report a concern without negotiating with three departments. Connect finance escalation with phishing triage, and make ownership clear when a request arrives by phone or messaging rather than email. Include the conversation, attachments, and callback details in the report so analysts can see how the request developed.
If money has already moved, call the bank promptly and follow the organization’s fraud-response process, including appropriate law-enforcement reporting. Preserve the instructions and transfer details so responders can act on them. Recovery isn’t assured; waiting for an internal investigation to finish can cost time the bank could use to try to stop the funds.
Test the reply thread and the follow-up call
An exercise built around an obviously malicious first email won’t tell you whether finance handles a believable conversation safely. Test the transition from a routine exchange to an unusual instruction.
For example, a controlled scenario can start with an availability check, introduce a supplier payment change, and then follow up with a call from the supposed account manager. Use safe test data and pre-agreed boundaries. The outcome to measure is whether the workflow holds when the request sounds inconveniently plausible.
Human-layer red team exercises let finance, support, and security practice their parts in the same attempt. Multichannel simulation can carry the request from email into a follow-up call, where a convincing voice may put more pressure on the person who paused the payment.
Record whether the employee used the trusted contact, reported the request, and put the transfer on hold before release. Also check what happened after the report: did finance get an answer in time? A low click rate won’t tell you whether any of those safeguards worked.
Investigate the request and the impersonation together
A suspicious payment request may come from a compromised supplier account or an attacker’s lookalike domain. Those paths require different actions: the real supplier may need to secure its mailbox, while an impersonation site can be reported for removal. Establish which one you’re dealing with before choosing the response.
Doppel’s campaign-level visibility helps investigators connect reported requests with related impersonation infrastructure. Security can examine the surrounding campaign while finance checks the transaction, instead of both teams working from different fragments of the same request.
Keep the finance and security records tied together. Record the requested beneficiary, the trusted contact used to verify it, the sender’s address, and any related portal or phone number. That gives responders a trail to investigate while finance decides which payments to hold.
Make the awkward callback routine
Finance employees should be able to say, “We verify every bank-detail change this way,” even when the request appears to come from the CFO. Make that rule clear to leadership as well as the people releasing payments.
Rehearse the awkward cases: the supplier who can’t wait, the executive who’s unavailable for a callback, and the payment cutoff approaching. Staff need to know who can hold the transfer and how to escalate when they can’t verify it.
Would your callback and approval checks hold up once the conversation gets convincing? Schedule a Doppel demo to explore finance scenarios that test payment changes, follow-up calls, and escalation.