Doppel is the Official Social Engineering Defense Partner of the San Francisco 49ers

A consultative evaluation guide for security teams

Doppel vs. Netcraft

Netcraft takes down the phishing site. Doppel disrupts the campaign behind it.

What is Netcraft?

Netcraft is a digital risk protection and anti-phishing provider focused on phishing detection, fraudulent domain disruption, and takedown operations.

May be a fit for

Organizations that prioritize phishing detection, fraudulent domain disruption, and takedown execution.

Areas of focus

Netcraft has a traditional focus on phishing detection and disruption, including malicious websites and domains. Its offering also emphasizes takedown operations and relationships with infrastructure and service providers.

What buyers may want to evaluate

  • Netcraft's approach centers on detecting and disrupting individual phishing assets. Buyers seeking campaign-level correlation should evaluate how related infrastructure is connected and surfaced across channels.
  • Coverage is centered on websites and domains. Buyers should evaluate depth across messaging platforms such as Telegram and WhatsApp, social media, telco, and the dark web.
  • Netcraft focuses on external digital risk. Organizations may need separate email security and human risk management vendors to see how external threats reach employees.
  • Buyers should compare the level of dedicated technical account management and customer success support available for complex enterprise environments.

Side by side

Doppel vs. Netcraft feature comparison

Doppel
NETCRAFT
Cross-channel threat campaign mapping
Threat Graph correlates related threats across channels to provide a unified view of attacker infrastructure and coordinated campaigns.
Limited. Correlates domains, phishing sites, and social into broader campaigns. Buyers should evaluate demonstration of a unified threat graph that maps relationships across full channel coverage into a single campaign-level view.
Protection across the digital attack surface
Continuously monitors and remediates threats across a broad range of digital channels, including domains, social media, dark web, messaging platforms, mobile apps, marketplaces, data broker sites, and telco environments.
Limited. Coverage is centered on phishing websites and fraudulent domains. Buyers should evaluate the scope of coverage and takedown capabilities across social media, telco, dark web, and other channels relevant to their organization.
Unified platform visibility
Unified visibility across DRP, Email Security, and Human Risk Management connects external threats with what’s reaching inboxes and targeting people, providing richer context and action across the social engineering attack chain.
Limited. Primarily focused on external digital risk and disruption. Without integrated email and human risk capabilities, organizations have less visibility into how external threats are reaching and impacting employees.
User experience
Modern workflows help security teams quickly investigate threats, pivot across related infrastructure, and understand campaign context with minimal manual effort.
Buyers should compare investigation workflows, the ability to pivot across related infrastructure, and the level of campaign context available to analysts.
Enterprise scalability
Purpose-built for large enterprises, combining AI-driven automation with white-glove support from dedicated technical account management and customer success to navigate complex environments and evolving needs at scale.
Supports many large enterprises through mature phishing protection, large-scale monitoring, and established takedown operations.

Due diligence

Questions to ask when comparing Netcraft alternatives

These help security teams evaluate fit regardless of which solution they're considering.

  1. 01Can you map attacker infrastructure across domains, social media, messaging platforms, mobile apps, marketplaces, and the dark web, or are threats investigated and resolved individually?
  2. 02How do you define and measure detection, mitigation, blocking, and takedown times? How do you balance automation with analyst expertise throughout the takedown process?
  3. 03How much manual effort is required to pivot related infrastructure and understand the broader campaign behind an alert?
  4. 04What visibility do you provide into messaging-led fraud, executive impersonation, exposed PII, telecom threats, and coordinated campaigns beyond traditional phishing domains?
  5. 05How does your platform connect external digital threats with email and human risk signals to show how attacks are reaching and targeting employees?

Why security teams choose Doppel over Netcraft

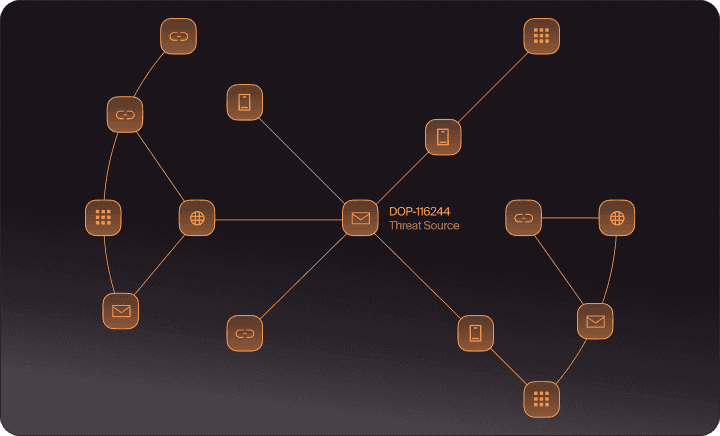
Doppel Threat Graph linking a threat source to related domains, emails, apps, and URLs

Understand the full campaign, not individual artifacts

The Doppel Threat Graph maps attacker infrastructure across channels in real time, helping security teams uncover relationships between threats across the digital attack surface. Rather than viewing potentially related indicators in isolation, Doppel provides campaign-level context to help security teams identify connected infrastructure and coordinate disruption efforts.

Doppel protecting a person across telco, dark web, domains, email, ecommerce, social media, crypto, apps, paid ads, and URLs

Protection across the digital attack surface

Doppel continuously discovers and remediates threats across domains, social media, messaging platforms, marketplaces, mobile apps, dark web, data broker sites, and telco environments. This broad coverage helps security teams identify and remediate threats across the channels most relevant to their organization.

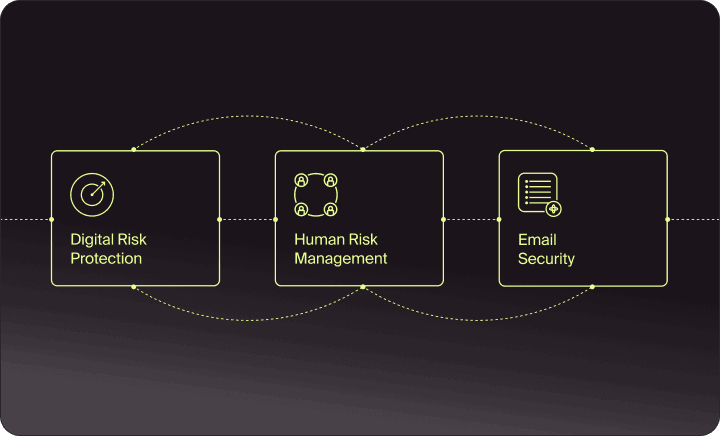
Doppel unified platform connecting Digital Risk Protection, Human Risk Management, and Email Security

Defend across the full attack chain

Doppel brings Digital Risk Protection, Email Security, and Human Risk Management together in one platform, connecting intelligence across external threats, inboxes, and human risk. This allows security teams to act on threats across multiple stages of the social engineering attack chain, from disrupting malicious infrastructure, to stopping threats in the inbox and strengthening defenses against human-targeted attacks.

What Doppel customers say

“I’ve used other services in the past. They’re great for domains, but not for Telegram, not for X. In less than three days [using Doppel], takedowns are completed. That’s amazing.”

Dudley Alan GrantAptos Foundation, Security Lead

Aptos Foundation
“We feel reassured that the Aptos Foundation has one of the strongest products available to actively take down the bad actors that are harming every organization’s security and brand reputation.”

Dudley Alan GrantAptos Foundation, Security Lead

Aptos Foundation
“Netcraft was missing threats across domains, apps, and social platforms, while its takedown model created more manual work and unexpected costs. Doppel surfaced what was being missed and gave us a much more automated approach to detection and takedowns.”

Security Leader, Gaming & Sportsbook

< 10 hours
Median takedown time
1 Billion
Signals analyzed daily
11M+
Verified alerts in 2025

Compare Doppel and Netcraft for Digital Risk Protection

See how Doppel protects the digital attack surface, connecting threats across channels and disrupting them from detection through takedown.

FAQs

What is the difference between Doppel and Netcraft?
Netcraft is traditionally focused on phishing detection and takedown for fraudulent websites and domains. Doppel's approach to digital risk protection includes cross-channel threat correlation, campaign-level visibility, and coverage across messaging, social, telco, and other channels, alongside integrated email security and human risk management.
Why is campaign-level visibility important in digital risk protection?
Attackers rarely rely on a single phishing site or impersonation account. Modern campaigns often span multiple domains, social platforms, messaging apps, and supporting infrastructure. Campaign-level visibility helps security teams identify relationships between these assets and coordinate disruption efforts across connected infrastructure, potentially increasing the time, cost, and effort required for attackers to reestablish a campaign.
How does Doppel investigate threats differently?
Doppel correlates related infrastructure across the digital attack surface using Threat Graph. This gives security teams context into the broader campaign across channels, helping identify connected threats and prioritize disruption efforts.
What types of threats should a digital risk protection platform cover?
Beyond phishing domains, many organizations look for protection across social media, messaging platforms like WhatsApp, mobile apps, marketplaces, dark web forums, data broker sites, telco environments, and more. Comprehensive visibility across these channels help security teams identify and remediate threats across a wider range of attack surfaces.
Why does a unified approach to social engineering defense matter?
External threats do not operate in isolation. The same campaign can span malicious infrastructure, employee inboxes, and human-targeted attacks. Doppel brings Digital Risk Protection, Email Security, and Human Risk Management together in one platform, connecting intelligence across these surfaces so security teams can identify related activity and take coordinated action at multiple stages of the attack chain.