Email click rates provide insight into user susceptibility on one channel, but they alone don’t reflect business risk. Inbox-only phishing simulations fail to consider the multi-channel nature of phishing attacks today – attackers are no longer sending plaintext emails, they’re conducting multistep phishing campaigns that traverse channels.
And by overrotating on email click rates, teams may be incentivized to run simple simulations that don’t accurately reflect business risk. A single mistake by a privileged user can cause far more damage than multiple clicks by low-risk users.
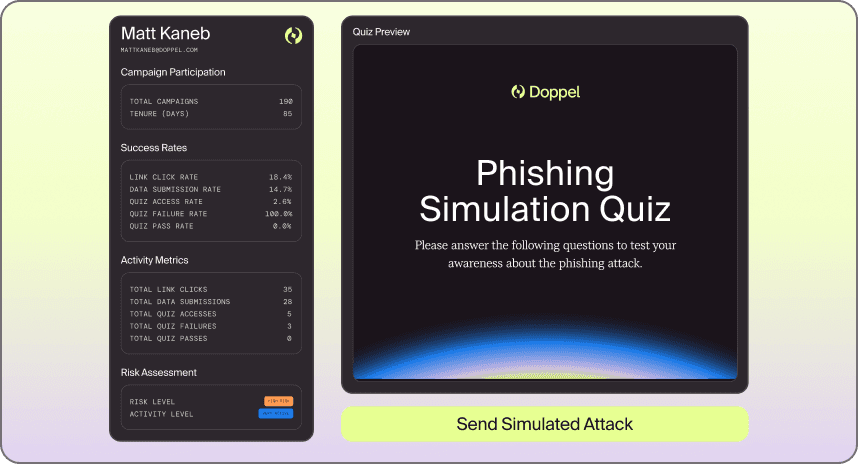
Doppel HRM simulations phishing attacks across email, voice calls, and messaging apps, to expose risk on every channel. Doppel uses dynamic risk modeling that factors in user role, access level, behavior, channel, and attack realism. This gives security leaders a clearer picture of where risk actually lives and where training will have the biggest impact.