Doppel is the Official Social Engineering Defense Partner of the San Francisco 49ers

The Doppel Myth-Buster

There’s a lot being said about Doppel

Funny thing about competitive claims: they work better when nobody checks them.

We’ve seen the comparison pages. We’ve heard the talking points. According to these mythmakers, Doppel only watches a handful of channels. Floods teams with alerts. Has no threat graph. Relies entirely on automation. And leaves customers to figure out the rest.

That would be concerning. If any of it were true.

So rather than trade FUD for FUD, let's set the record straight.

See Doppel for yourself
MYTH 01

“Doppel only monitors a narrow set of channels.”


FACT

Doppel covers a wide spectrum of the digital attack surface, including the hard-to-reach channels others may miss.


Doppel detects and disrupts threats across domains, social platforms, paid ads, messaging sources, telco, dark web, crypto, apps, email infrastructure, and more, all in one platform.

Because attackers don't stay neatly inside one channel.

An attack that starts with a malicious domain can jump to a fake social account, a paid ad, a phone number, or a messaging platform in minutes.

Doppel is built to follow the attacker across channels and connect that activity into the broader campaign, giving your team connected visibility across related activity.


The reality: Broad channel coverage. Fewer blind spots. One connected view.
Channels Doppel monitors, including domains, social, ads, messaging, phone, email, crypto, and apps
MYTH 02

“Doppel floods you with alerts.”


FACT

Comprehensive detection doesn’t have to mean alert fatigue.


Doppel is built to detect threats at scale across the assets, brands, executives, and infrastructure you’re protecting. We don’t reduce noise by sacrificing coverage. We reduce it by making the alerts we surface relevant and actionable.

Alerts are classified and prioritized so your team knows what requires attention, while the Threat Graph connects related activity across channels to disrupt the broader underlying campaign.

So even when Doppel uncovers a high volume of threats, your team gets the context to understand:

What matters → Why it matters → What it’s connected to → What to do next


Catch the threats. Cut the noise. Keep the context.

Alerts from email, chat, and phone prioritized into one protected view
MYTH 03

“Doppel doesn’t have a threat graph and stops at the artifact.”


FACT

The Threat Graph is core to how Doppel works.


Doppel’s Threat Graph links infrastructure across domains, social handles, phone numbers, paid ads, apps, and email infrastructure, forming these links into campaigns that surface the broader attack. We don’t just ask, “What is this artifact?” We ask, “What else is it connected to?”

One signal can reveal the infrastructure around it. A fake account can connect to a malicious domain. That domain can connect to a phone number. That phone number can reveal another part of the same campaign.

So what looks like one isolated alert becomes a map of the attack, giving your team the context to see:

The artifact → What it’s connected to → The broader campaign → Where to disrupt it


See the signal. Map the infrastructure. Disrupt the campaign.

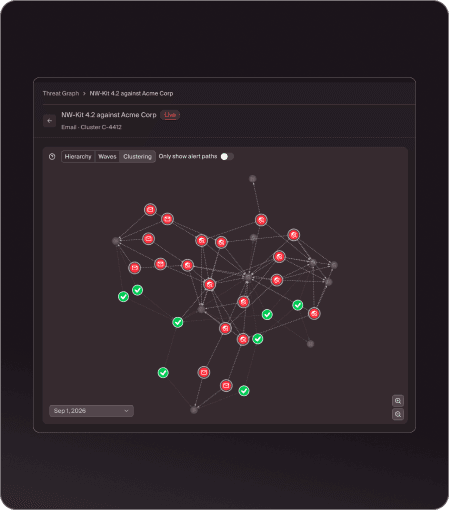
Threat Graph connecting related attack infrastructure into a campaign
MYTH 04

“Doppel starts every investigation from scratch.”


FACT

Every signal gets smarter with context.


Doppel continuously correlates signals across brands, channels, actors, and attacker infrastructure.

That context helps teams move beyond isolated incidents and understand threats at the campaign level, including relationships between infrastructure and patterns that might otherwise go unnoticed.

The point isn't to create a giant archive of everything we've ever seen.

It's to use connected intelligence to make new signals more actionable.

Because when attackers reuse infrastructure, tactics, and relationships, your defenses shouldn't have amnesia.


Security without context is just a queue.

Signals connected into shared context instead of isolated incidents
MYTH 05

“Doppel routes every alert to a human.”


FACT

Automation handles high-confidence workflows. Human expertise is there when the situation demands it.


Doppel uses agentic AI to automate investigation, correlation, prioritization, graph analysis, and eligible takedown workflows, reducing the manual work required to move from detection to disruption.

But not every threat fits neatly into an automated workflow. Complex cases, third-party limitations, and certain enforcement scenarios can require additional judgement or escalation.

Rather than forcing automation where it doesn’t work, Doppel brings in human expertise when it’s needed to keep the process moving. Our Applied Cyber team solves complex cases while teaching Doppel’s AI how practitioners approach these threats, making that expertise repeatable at scale.

That means automation handles scale and speed, while people help solve the exceptions.


Automate the repetitive. Escalate the important.

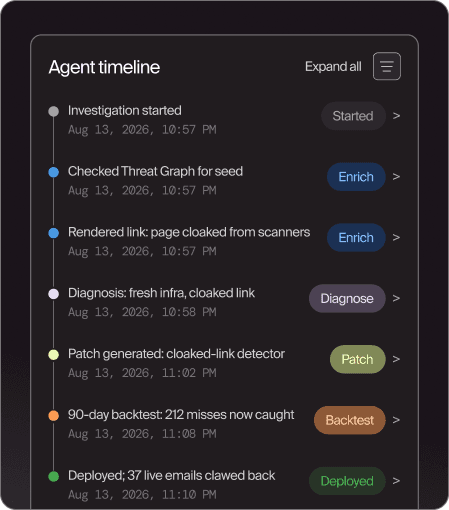
An agent timeline from investigation through diagnosis, patching, and deployment
MYTH 06

“Doppel is an automation-only black box.”


FACT

Doppel combines tailored protection, agentic AI, and human expertise.


Your Doppel environment isn't a copy-and-paste deployment. During onboarding, we configure the platform around your organization’s assets, executives, and brands, and what your team actually cares about protecting. That context informs what Doppel detects, prioritizes, and surfaces for your organization.

From there, agentic AI accelerates detection, correlation, prioritization, and disruption, automating the repetitive work that would otherwise fall on your security team.

And when automation reaches its limits, humans step in. If a third party doesn't support fully automated takedowns or an enforcement action requires escalation, Doppel analysts help move it forward.


Tailored to your organization. Automated wherever possible. Human-backed when it matters.

Layered protection that combines tailored coverage, automation, and human expertise

Social Engineering Defense

Here’s what competitors keep missing

Doppel isn't trying to build a slightly better version of yesterday's Digital Risk Protection platform. We're building Social Engineering Defense for an era where attacks move fluidly between brands, executives, domains, social platforms, phones, messaging apps, email, and people. That means connecting three things historically treated as separate problems:

Detect the attack

Find threats across the channels attackers actually use, and connect individual signals into the broader campaign.

Disrupt the infrastructure

Use AI-powered automation and human expertise to help disrupt the infrastructure behind impersonation, phishing, fraud, and social engineering.

Build resilience

Use realistic social-engineering scenarios in simulations and training designed to strengthen resilience against real-world attacks.

One connected defense against a connected threat.

See Doppel in action

Don't take our word for it

Our customers have already put these claims to the test

2 weeks vs. 1 year

“In just a two-week proof-of-concept, Doppel took down about half of what our incumbent solution did in an entire year.”


Zane LackeyGeneral Partner, Andreessen Horowitz Former CISO, Etsy

1,800+ malicious accounts and fraudulent domains taken down


Coinbase credits Doppel with helping take down 800+ malicious social media accounts and 1,000+ fraudulent domains while streamlining its approach to brand protection.

Weeks → minutes


ARK Invest reported cutting scam takedown times from weeks to minutes and reducing impersonation volume by 50% year over year with Doppel.

Protection on autopilot


“Doppel enables us to put brand protection and anti-phishing security on autopilot.”

Steve KrauseSVP, Deputy General Counsel, Dapper Labs

Browse our case studies

See for yourself

Competitor pages are marketing.

This one is too.

The best way to compare is putting the products side by side.

Bring us your hardest use case.

Bring us the threat your current platform missed.

Bring us the claims you've heard about Doppel.

We'll show you how Doppel handles it.

Get Your Personalized Demo

Fill out the form below and our team will contact you within 24 hours to schedule your demo.

By submitting this form, you agree to receive communications about our products and services

Compare

Doppel vs. Adaptive Security

Compare Doppel vs. Adaptive Security across multi-channel phishing simulations, security awareness training, human risk scoring, content creation, and support.

Doppel vs. Hoxhunt

Compare Doppel vs. Hoxhunt across multichannel phishing simulations, security awareness training, human risk scoring, threat intelligence, and support.

Doppel vs. KnowBe4

Compare Doppel vs. KnowBe4 across multi-channel phishing simulations, security awareness training, human risk scoring, AI personalization, and support.

Doppel vs. Netcraft

Compare Doppel vs. Netcraft across digital risk protection, phishing detection, threat intelligence, campaign mapping, takedowns, and enterprise scale.

Doppel vs. Outtake

Compare Doppel vs. Outtake across digital risk protection, threat intelligence, attack surface coverage, automated takedowns, analyst support, and scale.

Doppel vs. ZeroFox

Compare Doppel vs. ZeroFox across digital risk protection, campaign disruption, agentic automation, alert triage, messaging-platform coverage, and analyst support.