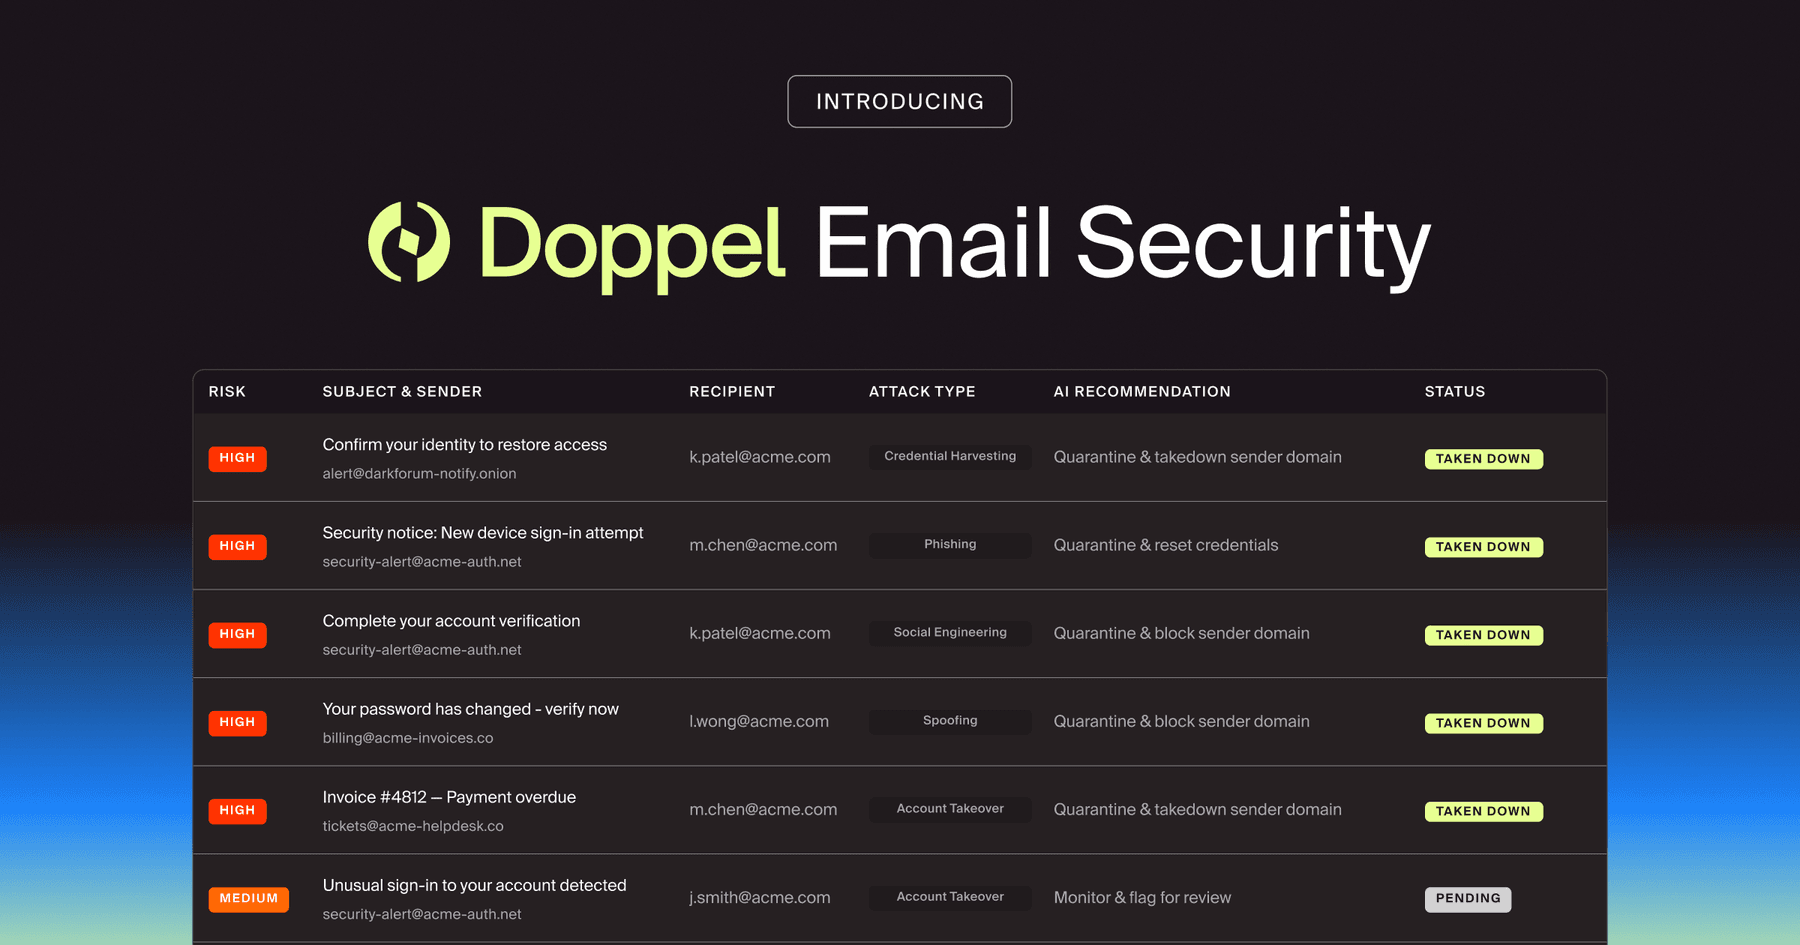
Doppel Email Security is now generally available
The agentic email security solution that empowers you to fight back against social engineering attacks. Detection isn't enough. Disruption is the difference.
Red teams are a critical piece of a mature security program, designed to emulate adversary tactics to identify and remediate the risk of malicious, negligent, or ignorant employees. Traditional red teaming, though, is resource-heavy and manual. Doppel provides a scalable way to pressure-test employees against the tactics that attackers are using everyday, across every channel.
The reality: Adversaries are resource-rich. Modern social engineering campaigns combine phishing, vishing, smishing, impersonation, and targeted pretexts across multiple channels simultaneously.
Red teams and pen testers that rely on manual exercises, expensive consultants, or single-channel testing often struggle to keep pace with highly motivated and resource-rich attackers. The result is an uphill battle to validate employee readiness and eliminate insider risk.
8.8 minutes is the average conversation with a human agent
15% of calls leaked information about internal processes
92% of calls perceived as human
12% violated internal protocols
7 organizational technology leaks
Hyper-sophisticated conversational threading
Insider risk management at scale
AI-powered or human-led red teaming
Behavioral Measurement & Targeted Interventions
Adversaries prey on weak spots within an organization. That could mean scouring the dark web for leaked credentials, or brute forcing their way into unprotected systems. But often, they take a more manipulative approach: using emotion or urgency to convince an employee to grant legitimate access or reveal key information. And attackers are persistent, following up on existing threads, responding in near real-time, and changing tact when they hit a wall.
Red teaming is the only way for an organization to predict how their employees respond in those scenarios. Red teaming reveals which users keep their defenses up even as the playing field evolves, and which may fall victim to deceptive campaigns or lucrative offers.
Doppel unlocks red teaming at scale, with human-led or AI-powered dynamic exchanges that test how employees react in evolving scenarios, and provide clear visibility into risk levels across the organization.
Red Teaming At Scale
Clear Visibility Into Risk
Increased Operational Efficiency
Higher Protocol Compliance
Download eBook
Download eBook
Download Datasheet
Traditional red teams rely on manual workflows and human-only interactions. Doppel empowers red teams to scale with AI-powered or human-led interactions, seamlessly carrying out pen testing and red teaming across channels, while Doppel handles the infrastructure. Doppel is anchored in Social Engineering Defense (SED)—focusing on multi-channel protections, impersonation detection, and human workflow strengthening. We test across email, voice, SMS, social media, and messaging to mirror how modern adversaries actually operate.
Yes. All simulations are controlled, scoped, and designed to improve resilience and response behavior. Outcomes focus on systems and workflows—not blame. Doppel follows responsible disclosure practices, obfuscates sensitive information, and works within your organization's policies.
Success means stronger verification behaviors, faster escalation times, higher reporting rates, and measurable reductions in risky behaviors—tracked over time as part of your Human Risk Management (HRM) program. You get executive-ready reports and insights with clear findings tied to specific users, teams, channels, or patterns.
The cadence of red teaming exercised depends largely on the intended outcome. We recommend conducting penetration testing and red teaming designed to identify gaps in awareness on a continuous or quarterly basis. Social engineering tactics evolve rapidly—especially with AI-generated content—so ongoing testing ensures your defenses stay current and your teams maintain readiness. However, red teaming geared toward identifying insider risk can be done on a more limited scale, but on a more regular basis, given the sensitive and urgent nature.
Yes. Doppel Simulation can incorporate synthetic voice clones, AI-generated messaging, and sophisticated pretexts that mirror the latest adversary techniques—giving your team realistic exposure to threats they will increasingly face, and allowing security teams to see how they perform.
Download eBook
Download eBook
Download Datasheet