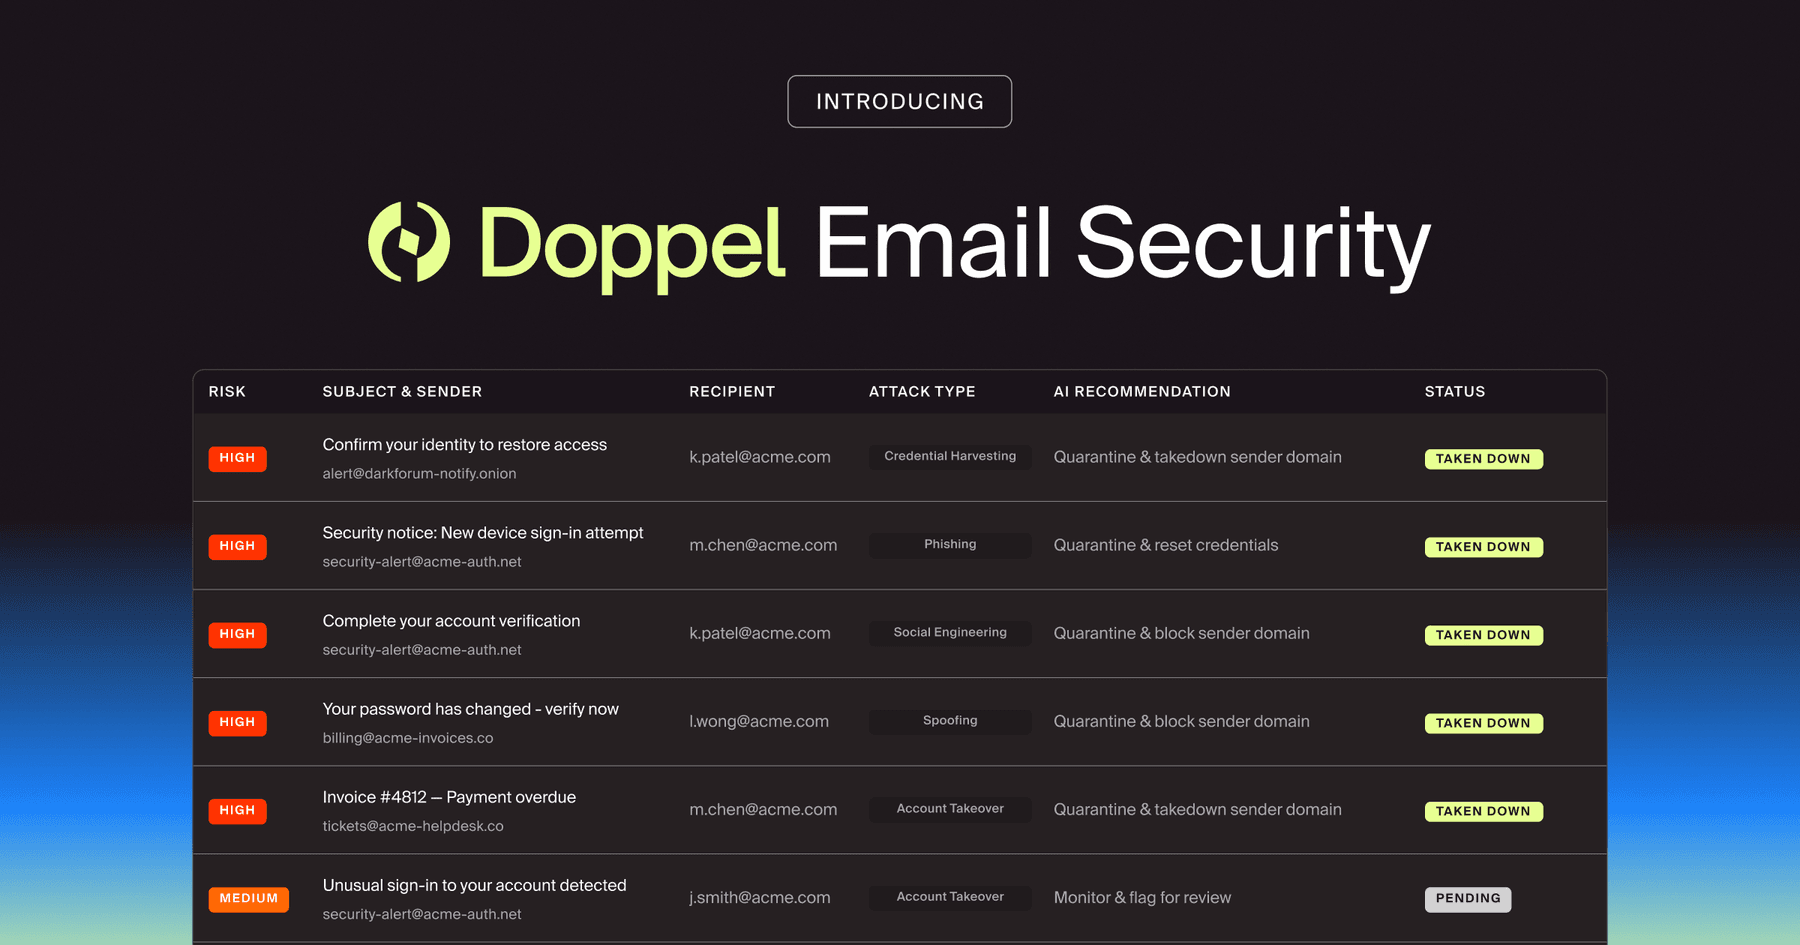
Doppel Email Security is now generally available
The agentic email security solution that empowers you to fight back against social engineering attacks. Detection isn't enough. Disruption is the difference.
Executives and high-profile employees are prime targets for impersonation, social engineering, and digital exposure. Doppel helps organizations identify, monitor, and mitigate threats targeting leadership before they escalate into security incidents, financial loss, or reputational damage.
Your leaders are high-value targets. Executives and key personnel hold privileged access, influence major decisions, and represent the public face of your organization.
When executives are targeted, the consequences can cascade across the organization. Threat actors frequently impersonate executives to launch phishing campaigns, manipulate financial transactions, or gain unauthorized access. Exposed personal data and deepfake impersonations don't just impact the individuals.
Detect threats targeting executives
Reduce executive exposure
Disrupt executive impersonation and abuse




Protect leadership from targeted threats
Prevent attacks from spreading across the business
Safeguard brand reputation and trust

Download Datasheet

Download Datasheet
Download eBook
Executives have access to sensitive information, financial authority, and public visibility—making them highly valuable targets for attackers seeking financial gain, access, or influence.
Common threats include impersonating social accounts, phishing and social engineering attacks, doxxing attempts, exposed personal information (PII), and deepfake campaigns.
Doppel monitors across the open web, social media platforms, domains, marketplaces, messaging apps, and underground communities where attackers plan and execute campaigns.
While CEOs or CFOs are common targets, attackers often focus on anyone with authority, public visibility, or access to sensitive systems. This can include founders, board members, senior leadership, and other key personnel involved in financial approvals or strategic decision-making.
Attackers often collect publicly available information from social media, data broker sites, breached databases, and public records. This information can be used to craft convincing impersonation attempts, launch social engineering attacks, or target executives with harassment and doxxing campaigns.
Download Datasheet
Download Datasheet
Download eBook