Planning your move from KnowBe4? Start here

Red Teaming

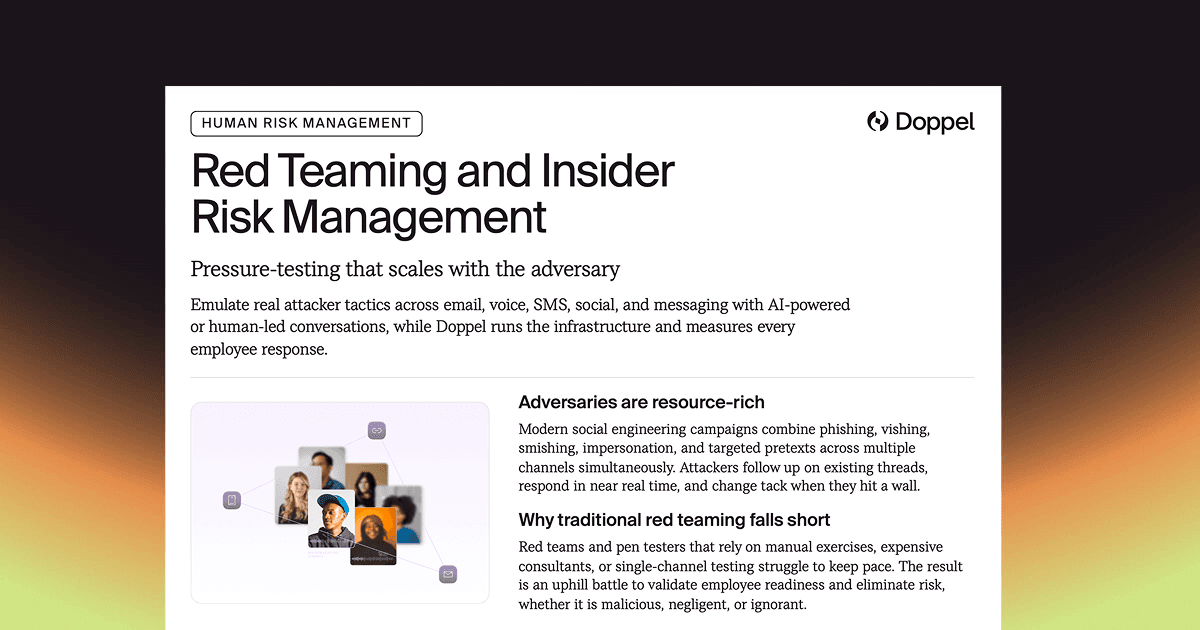
Red team your people, agents, and processes

Doppel runs realistic, continuous social engineering tests against employees, help desks, and AI agents. Find where people and agents break, then retest as defenses evolve.

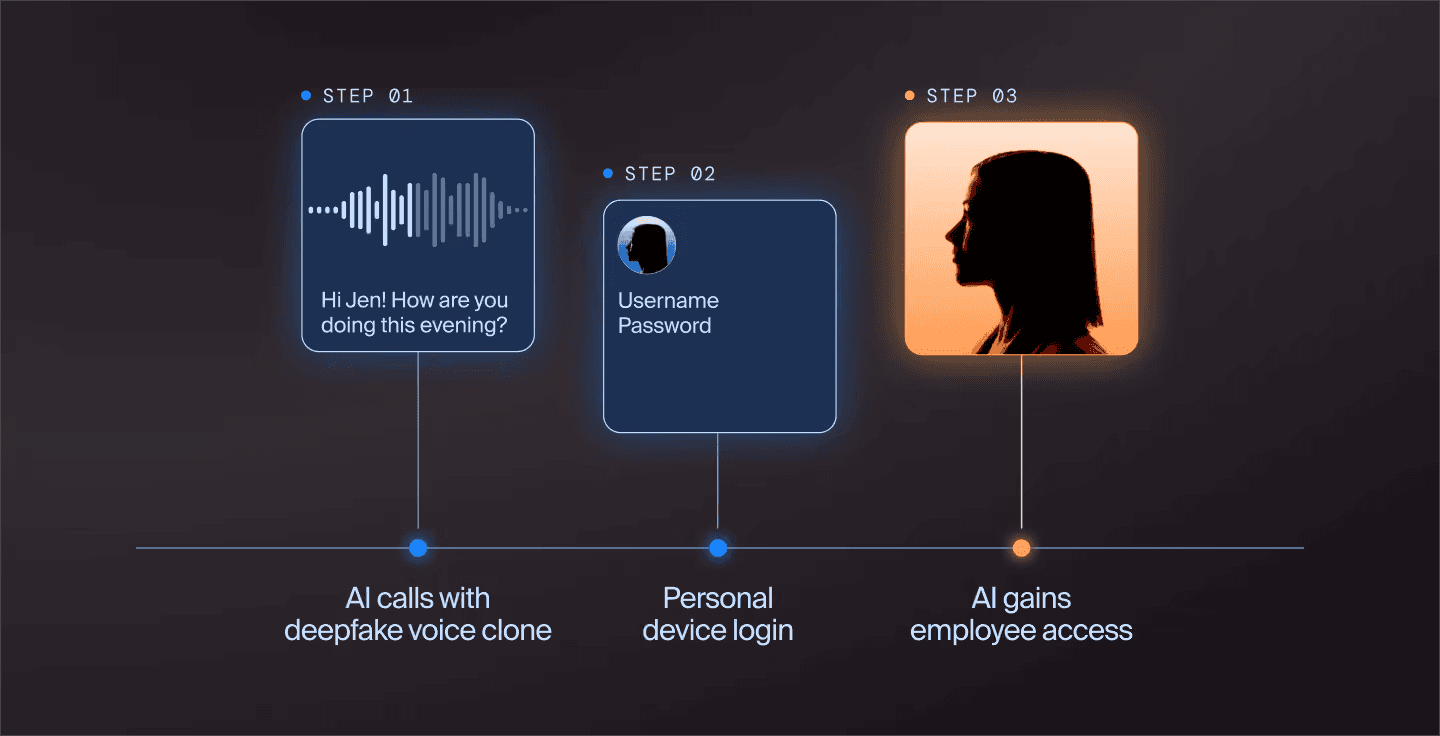
AI deepfake voice call leading to a personal device login and employee access
Protecting the best brands
ARK Invest
BlackRock
Coinbase
Ramp
OpenAI
CBRE
Notion
United Airlines
49ers
Knicks
Shopify
Tripadvisor
Vy Capital
Urban Outfitters
Klaviyo
Orrick
Andreessen Horowitz
Poshmark
Cyera
Aptos Foundation
Why Red Teaming

Your attack surface now includes people, AI agents, and processes

Attackers increasingly manipulate the same interfaces customers and employees trust: people, contact centers, voice agents, and conversational systems. One-time manual assessments can’t keep pace as models, prompts, workflows, and social engineering tactics change continuously.

Outcomes

Find the weaknesses attackers will exploit before they do

Shield connected to device, link, and web attack vectors

Red team humans and AI agents

Test employees, helpdesks, contact centers, and AI agents against realistic social engineering designed to break business rules, bypass verification, expose sensitive data, or trigger unauthorized actions.

Many employees targeted across email, phone, and messaging channels

Test at the scale attackers operate

Use AI-driven conversational red teaming to run repeatable, dynamic tests across large populations and workflows, while human-led conversations bring expert judgment and creativity to bespoke, high-value scenarios.

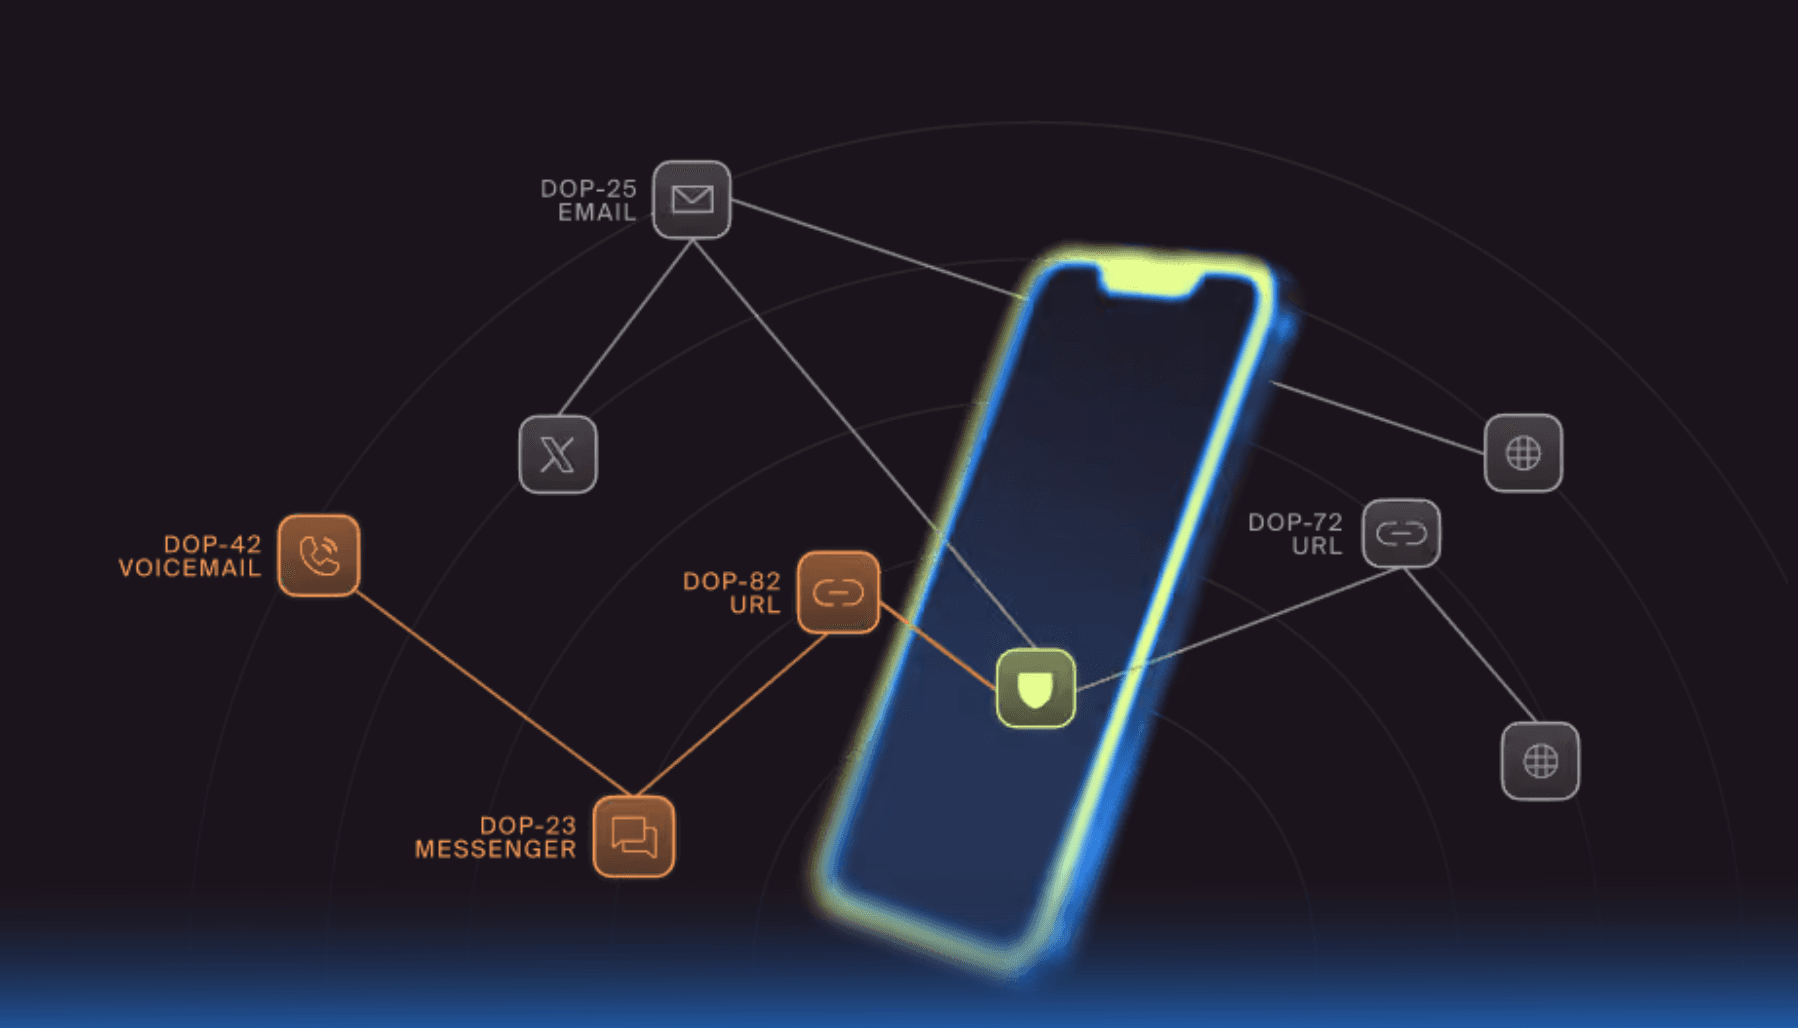
Phone connected to a graph of email, voicemail, messenger, and URL attack vectors

Keep testing as defenses change

Move beyond point-in-time engagements with repeatable red teaming that can validate fixes, expose regressions, and reveal new weaknesses as people, agents, policies, and workflows evolve.

How it works

Red teaming and penetration testing built for dynamic social engineering

Doppel combines AI-driven conversational testing, human-led engagements from your security team or our managed service, and multichannel simulation infrastructure to pressure-test the people and agents that attackers target. Define the objective and guardrails, run realistic conversations at scale, capture the decisions and rule violations that matter, then retest to verify whether defenses actually improved.

1. Choose the target

Test employees, helpdesks, contact centers, AI voice agents, and supported conversational workflows against realistic adversarial scenarios.

2. Decide how to engage

Use AI-driven conversational testing for scale and repeatability, human-led conversations for expert creativity and bespoke scenarios, or combine both approaches.

3. Test real business rules

Probe whether a human or agent discloses sensitive information, bypasses identity checks, executes an unauthorized action, or otherwise violates the policies the workflow is designed to enforce.

4. Retest continuously

Re-run scenarios as prompts, policies, models, employees, and workflows change to verify fixes and detect regressions over time.
Red team across critical workflows

Red team both the human and agent attack surface

The same attack can expose very different weaknesses depending on who or what is on the other end. Doppel runs realistic social engineering attacks against both humans and agents to see whether people follow the process and whether AI agents stick to their rules.

Human judgment and process

Run realistic scenarios against employees, executives, helpdesks, contact centers, and outsourced teams across voice, SMS, email, collaboration tools, and other supported channels to pressure-test protocol adherence.

Agent guardrails and business logic

Pen test your AI agents at scale to see whether they can be tricked into sharing information, skipping verification, taking unauthorized actions, or breaking your business rules.
See it in action

To learn how Doppel can help scale your red teaming and pen testing, connect with our team.

FAQs

Frequently Asked Questions

What is red teaming?

Red teaming is a security testing practice that simulates realistic attacker behavior to uncover weaknesses in people, processes, systems, and controls before a real adversary can exploit them.

In social engineering, that can include testing how employees, helpdesks, contact centers, and AI agents respond to manipulation, impersonation, and high-pressure requests.

How does Doppel support red teaming?

Doppel helps organizations run realistic, repeatable social engineering red-team exercises across humans and AI agents. Teams can use AI-driven conversational testing for scale and consistency, human-led testing for bespoke or high-value scenarios, or combine both approaches.

Doppel also supports multichannel testing across voice, SMS, email, collaboration tools, and other supported communication surfaces.

Are penetration testing (pen testing) and red teaming the same thing?

No, though they are closely related. Penetration testing typically focuses on finding and validating technical vulnerabilities in systems, applications, or networks. Red teaming takes a broader, adversarial approach and tests whether an attacker can achieve a real-world objective by combining multiple techniques, including social engineering.

Doppel focuses on the human and conversational side of red teaming: testing how people, AI agents, and business workflows respond under realistic attack conditions. Some describe their work with Doppel as pen testing for AI agents, as they blur the line between technology and behavior. Explore our recent blog post to learn more.
How does AI-agent red teaming work?

Doppel’s agents engage AI voice agents in realistic, multi-turn conversations with a defined adversarial objective. The goal is to determine whether the target agent can be manipulated into breaking a business rule: for example, bypassing verification, disclosing sensitive information, misusing a workflow, or taking an unauthorized action. Findings can then be used to improve guardrails and retest the agent as its prompts, policies, and capabilities evolve.

Can Doppel red team humans and AI agents?

Yes. Doppel can red team human targets such as employees, executives, helpdesks, contact centers, and outsourced teams, as well as AI voice agents. The same red-team program can test different targets using AI-driven or human-led conversational approaches, helping security teams understand where both people and automated systems are vulnerable to social engineering.

Learn how Doppel can protect your people, processes, and brand from social engineering attacks

Join hundreds of companies already using our platform to protect their brand and people from social engineering attacks.