Doppel is the Official Social Engineering Defense Partner of the San Francisco 49ers

Risk Signal Ingestion

One risk score, built across security signals

Bring real-world identity, access, and security signals into Doppel to understand where risk lies, why, and what to do next.

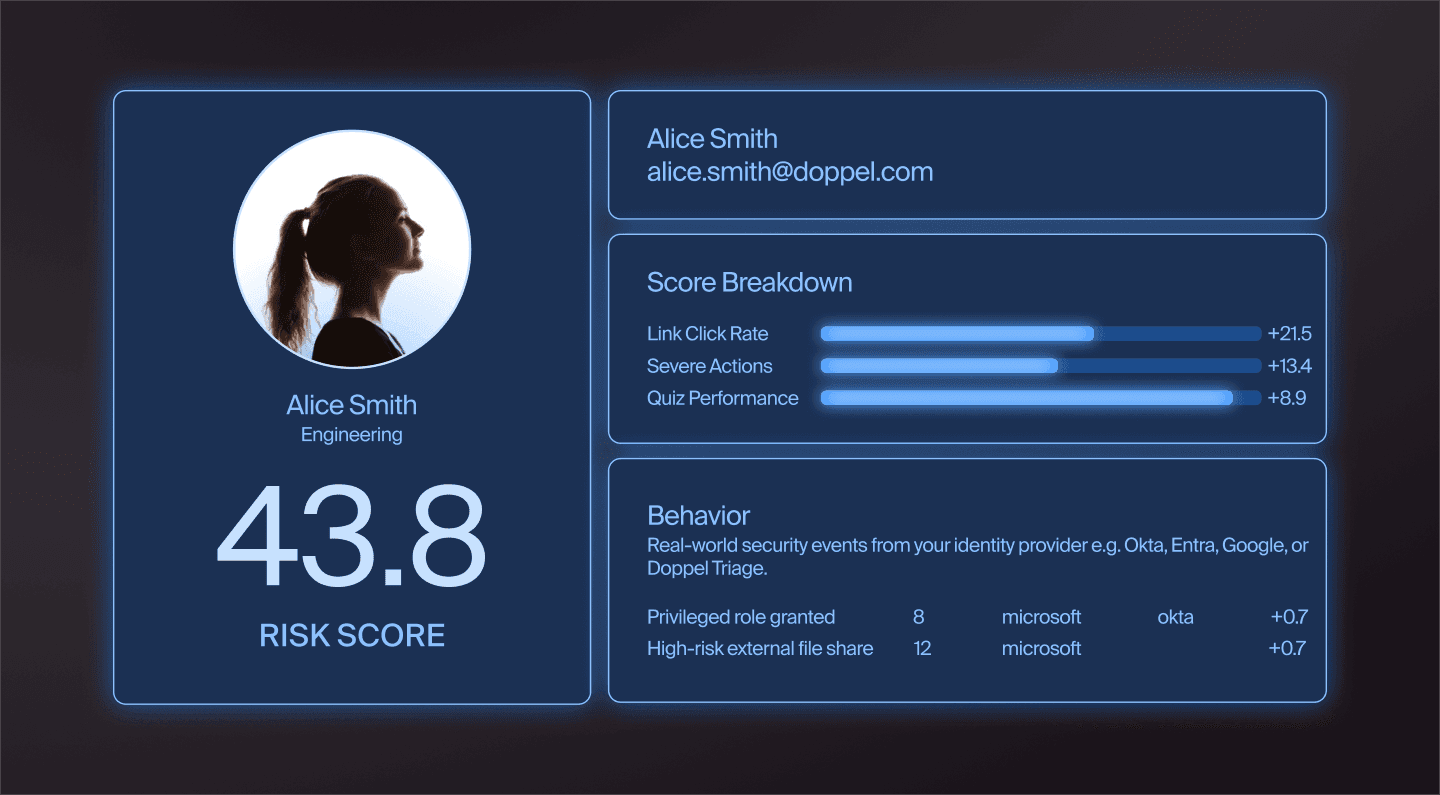
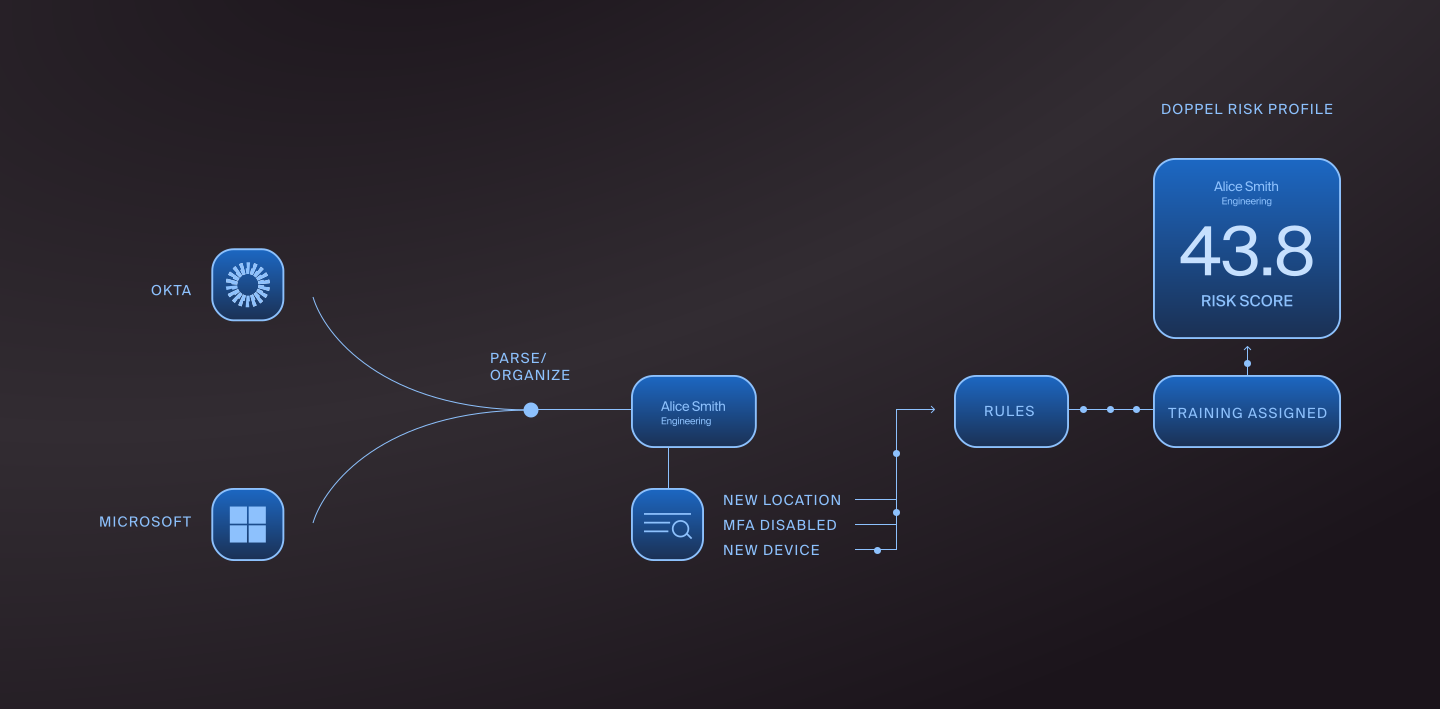
Doppel risk score with contributing external security signals
Protecting the best brands
ARK Invest
BlackRock
Coinbase
Ramp
OpenAI
CBRE
Notion
United Airlines
49ers
Knicks
Shopify
Tripadvisor
Vy Capital
Urban Outfitters
Klaviyo
Orrick
Andreessen Horowitz
Poshmark
Cyera
Aptos Foundation
Why Risk Signal Ingestion

Human risk is bigger than a phishing click

Simulation results and training completion only tell part of the story. Your security stack already contains critical signals about employee risk: from suspicious sign-ins and MFA resets to elevated privileges and account changes. Doppel Risk Signal Ingestion unifies those signals, connecting the insights from across your security stack to your human risk management program.

Outcomes

Know who is at risk. Understand why. Take action.

Prioritize the people who need attention

Prioritize the people who need attention

Simulation results are an important signal, but employees with similar results can have different risk indicators. Bring relevant identity and access events alongside behavior to see who may need a closer look.

Understand what’s driving risk

Understand what’s driving risk

Go beyond a black-box score to see the behaviors and security signals contributing to each employee’s risk profile. Give your team the context to assess the best way to shape human behavior.

Deliver smarter interventions

Deliver smarter interventions

Use real-world changes in behavior and security signals to inform targeted simulations, training, and other interventions, so your next step reflects what you’re seeing, rather than relying only on a fixed schedule.

How it works

Put your security signals to work

Risk Signal Ingestion connects Doppel to the security systems you already use and brings relevant identity and access events into each employee’s risk profile. Doppel ingests those signals, maps them to the right user, and evaluates them alongside the behaviors your team is trying to shape through simulations, training, and phishing reporting.

The result is a continuously updated view of employee risk indicators, what is driving that risk, and where intervention is needed.

Connect

Authorize read-only access to supported security systems.

Correlate

Normalize relevant events and map them to the right user.

Understand

Add real-world security context to Doppel’s behavior-driven risk model.

Act

Use changes in risk to inform targeted simulations, training, and other interventions.
Risk model

A risk score built on behavior, not isolated events

Not every event carries the same risk, and not every click carries the same weight. Doppel evaluates patterns of behavior alongside security context to build a risk score that helps assess susceptibility and exposure.

Severity-aware

Higher-impact behaviors and signals carry more weight.

Recency-aware

Recent activity matters more, while older signals decay over time.

Context-aware

Risk is evaluated against the circumstances surrounding the user and event.

Explainable

Understand which behaviors and signals are contributing to an employee’s risk.
Signal sources

Bring real-world security context into every risk score

Your identity and access systems already contain signals that can help you understand employee risk. Doppel brings that context into HRM, connecting security events with the people behind them and the behaviors we observe directly.

Authentication activity

Understand relevant sign-in activity, including successful and failed authentication events.

MFA and credential changes

Capture events like MFA enrollment or disablement, password resets, and credential changes.

Account and privilege changes

Add context from account lifecycle events, group and application assignments, and privilege grants.
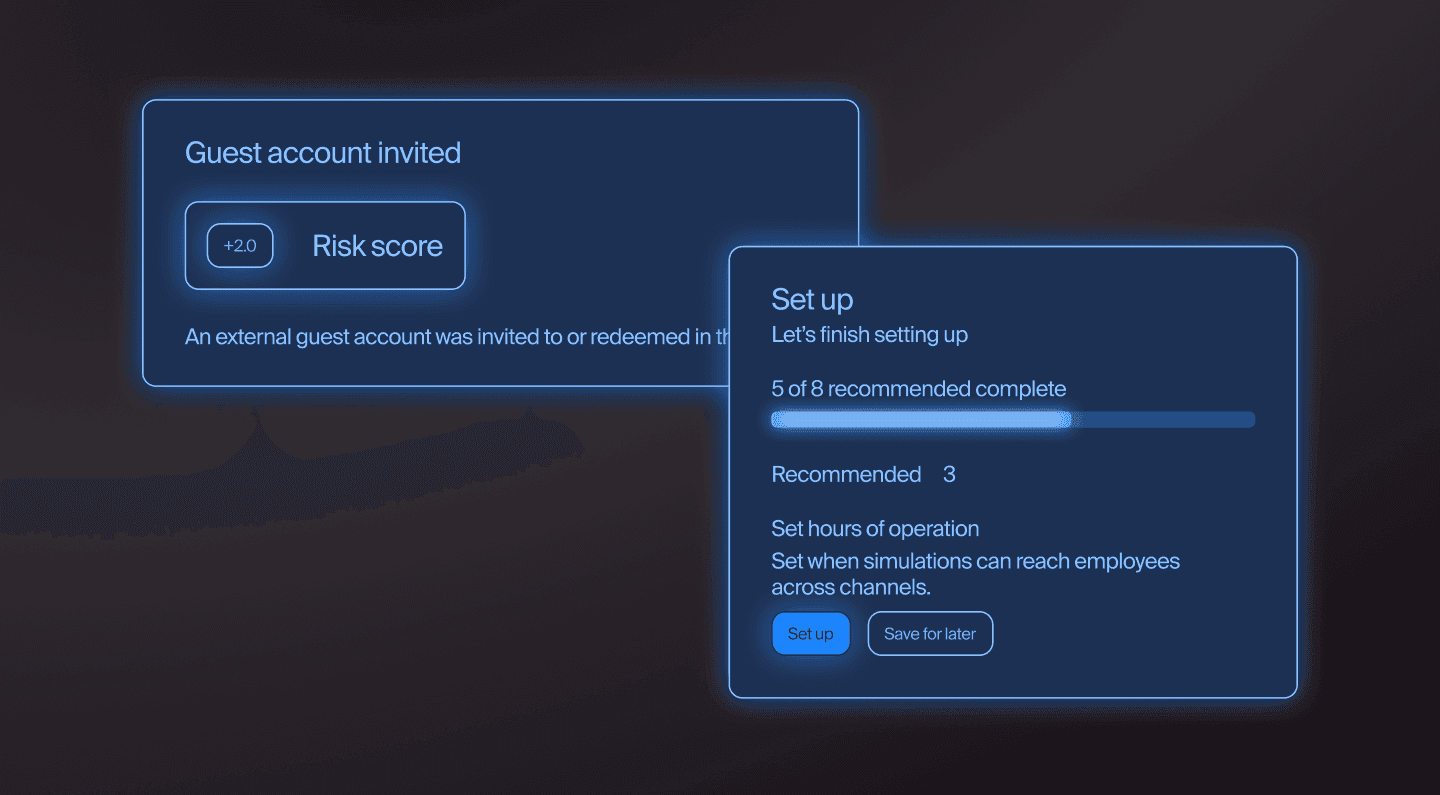
Incorporate relevant application consent activity into the user’s broader risk profile.
Integrations

Available at launch

Direct integrations with Okta and Microsoft Entra ID. Additional integrations are on the roadmap.

FAQs

Frequently asked questions

What is Risk Signal Ingestion?

Risk Signal Ingestion is a Doppel HRM capability that connects to your existing security systems and incorporates their identity and access events into each employee's risk profile.

Which integrations are available?

At launch, Doppel supports direct integrations with Okta and Microsoft Entra ID for relevant identity and access events.

Does every security event change someone's risk score?

No. Doppel evaluates signals contextually using transparent rules, severity weighting, recency, and patterns over time. A single event does not automatically make an employee high risk.

Does external data replace Doppel simulation behavior?

No. External signals supplement the behavior Doppel directly observes through simulations, training, and phishing reporting.

Is Risk Signal Ingestion read-only?

Yes. Initial integrations use least-privilege, read-only access to relevant security logs.

What data does Doppel collect?

Doppel collects relevant event metadata. It does not collect mailbox contents, files, documents, or message bodies through Risk Signal Ingestion.

Learn how Doppel can protect your brand from social engineering attacks

Join hundreds of companies already using our platform to protect their brand and people from social engineering attacks.